An accountable practice across security, frameworks and AI.
Inline Code is run by a certified offensive and defensive security practitioner with a platform engineering background, who also sits in the accountable officer seat for clients. That combination is the practice: we can find the flaw in a system, AI or otherwise, build the control that closes it, and then answer to your board for what is left.
We work with Australian enterprises and regulated organisations across financial services, healthcare, professional services, technology, hospitality, and government supply chain: anyone who needs someone accountable for their security, the frameworks they are measured against, and the AI they are putting to work.
Practitioner
Who you work with.
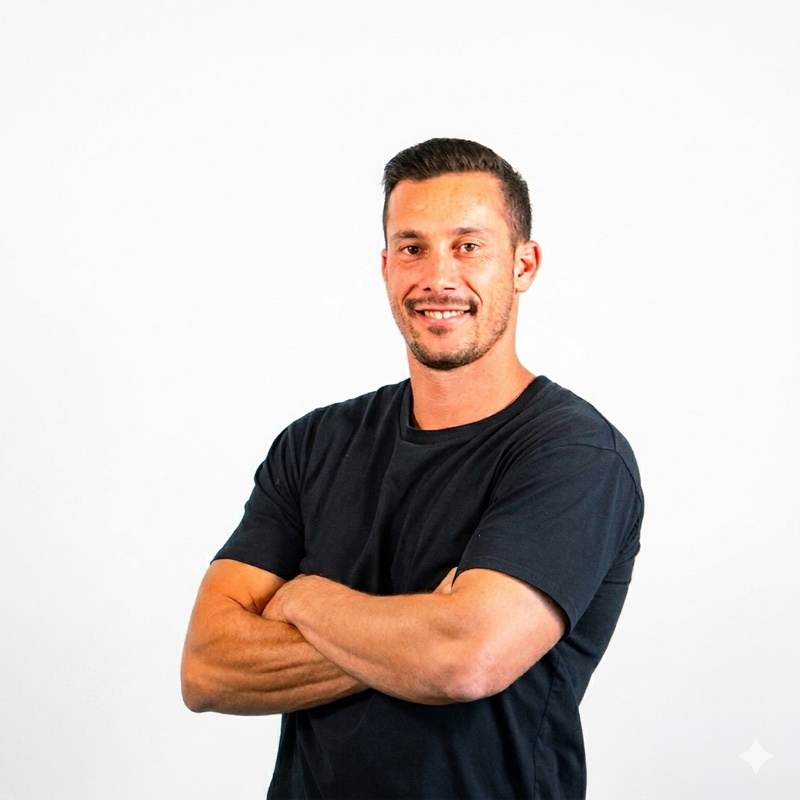
Mathew Sayed is the founder of Inline Code and the practitioner who delivers each engagement. Mathew is a certified offensive and defensive security practitioner with experience across financial services, government, and regulated mid-cap technology firms.
His work spans the full security lifecycle: penetration testing, red team operations, defensive architecture, compliance program design, and now AI governance and information risk leadership.
The Inline Code practice exists because the AI governance market is full of policy writers and tool vendors. It is short on practitioners who can both produce a board pack and configure an admin console. Mathew operates at both ends of that range.
Practice areas
- Fractional CISO
- Incident response leadership
- APRA CPS 234 and CPS 230
- ISO/IEC 42001 implementation
- Offensive and defensive security
- AI governance and risk
- AI offensive security and red teaming
- Agent containment and AI defence
Position
What we believe.
Security and AI governance done well is operational. The frameworks exist. The standards exist. What is missing in most organisations is a named individual who carries accountability and the practitioner skill to translate frameworks into controls that actually work day to day.
We do not produce policies that cannot be implemented. We do not run open-ended discovery engagements. We do not chase AI hype and we do not deny it. We do the work that lets your board sleep, your auditor sign, and your staff use the tools you have purchased.
What we will not do
Where we push back.
Five things we say no to. Naming them up front saves both of us time.
Compliance theatre
We do not produce documents that satisfy auditors but produce no operational change.
Framework dumping
We do not deliver long policies without an implementation roadmap.
Vendor capture
We do not recommend tools without an articulated control objective.
Over-scoping
We do not specify controls that a mid-market client cannot realistically operate.
Shadow AI denial
We do not write governance documents that pretend staff are not using personal AI accounts.
Get started
Talk to the security lead who would do the work.
A thirty-minute discovery call costs nothing. We confirm fit, scope, and timing, then issue a fixed-fee statement of work within two business days.